For regulated UK organisations
Independent cyber security consultancy.One partner accountable for all of it.
We assess your risk, choose the right specialists and technology, oversee delivery and keep you audit-ready.
How we work
Your organisation
Threat Protect
One point of accountability
- MDR and SOC providers
- Penetration testers
- Assessment partners
- Virtual CISOs
- AI governance specialists
- Technology vendors
- Assess
- Choose
- Oversee
- Evidence
Threat Protect is a UK cyber security advisory firm. It is vendor-agnostic: it gives independent security and compliance advice, then selects, contracts and oversees specialist providers for each service, acting as the client’s single point of accountability.
AI services
Your people are probably using AI already. Who is governing it?
Find out where AI is in use, set the rules, test what you build or connect, and evidence it for your board, auditors and customers.
Explore AI services- Govern the AI your people use
- Manage the risk
- Secure the AI you build or connect
- Prove it
- AI spend management
Why Threat Protect
Independent advice. One partner accountable.
Evidenced for your auditors.
of client audits passed, year after year
Independent advice
Vendor-agnostic by design. We recommend what genuinely fits your company and your risk, and only what you need, and often that means getting more from what you already have.
One point of accountability
We assemble and direct the specialists who run your security and compliance: 24×7 managed detection and response, and continuous compliance that keeps your evidence current year-round, with one team accountable to you.
Evidenced for auditors
Audit-ready proof as you go, so no audit becomes a last-minute rush. Continuous compliance delivered through certified assessment partners, so the answer is always ready when a client or regulator asks.
What we do
One partner for protection, compliance and governance.
Independent advice, the right technology, round-the-clock monitoring from specialist providers, and compliance kept audit-ready all year, through one accountable partner. Pick a starting point, or let us help you choose.
Advisory & Consulting
Senior, vendor-agnostic security leadership: a clear read of where you stand, a board-ready risk picture, and a costed roadmap that fixes what matters first.
More on AdvisoryManaged Security
Managed detection & response, endpoint and email, run around the clock by specialist providers we select and oversee, so your team does not have to.
More on Managed SecurityContinuous Compliance
A monthly subscription that keeps you audit-ready all year: Cyber Essentials, ISO 27001, SOC 2, DORA and NIS2, delivered through certified assessment partners.
More on ComplianceAI Services
Govern and secure your own use of AI: shadow AI, AI policy, Copilot readiness, supplier risk, application testing, ISO 42001 readiness and EU AI Act preparation.
More on AI servicesTechnology & Solutions
Best-of-breed security technology organised by the problem it solves, not by vendor: email, endpoint, identity, network, awareness and cyber insurance.
More on TechnologyYour Security Buyer
We hold partner agreements across the market, so we secure preferential rates and stay free to recommend what genuinely fits. One buyer, every vendor conversation handled.
More on sourcingHigh-risk AI obligations apply from December 2027. Use the time well.
The EU AI Act is phasing in now, and its transparency duties already apply. Obligations for high-risk uses such as recruitment, credit and education were pushed back to 2 December 2027. The extra time is a window to build audit-ready AI governance properly, not a reason to wait.
Plan your AI Act readinessSectors
Built for regulated sectors where the pressure is highest.

Finance
Wealth managers, asset managers and financial companies carry more cyber obligation than almost anyone: FCA and PRA expectations on operational resilience, named accountability under SM&CR, and fraud pressure that never lets up.
Explore
Legal
Client confidentiality is the whole business, and law firms are squarely in attackers’ sights for payment diversion and conveyancing fraud.
Explore
Energy
Critical infrastructure, converging IT and operational technology, and a competent authority that expects evidence make energy a high-stakes security environment.
Explore
Pharma
Valuable intellectual property, regulated data integrity and complex supply chains put pharma and life sciences under sustained, sophisticated attack.
Explore
Healthcare
Patient data is among the most sensitive there is, and healthcare providers face the Data Security and Protection Toolkit, CQC scrutiny and relentless ransomware pressure.
Explore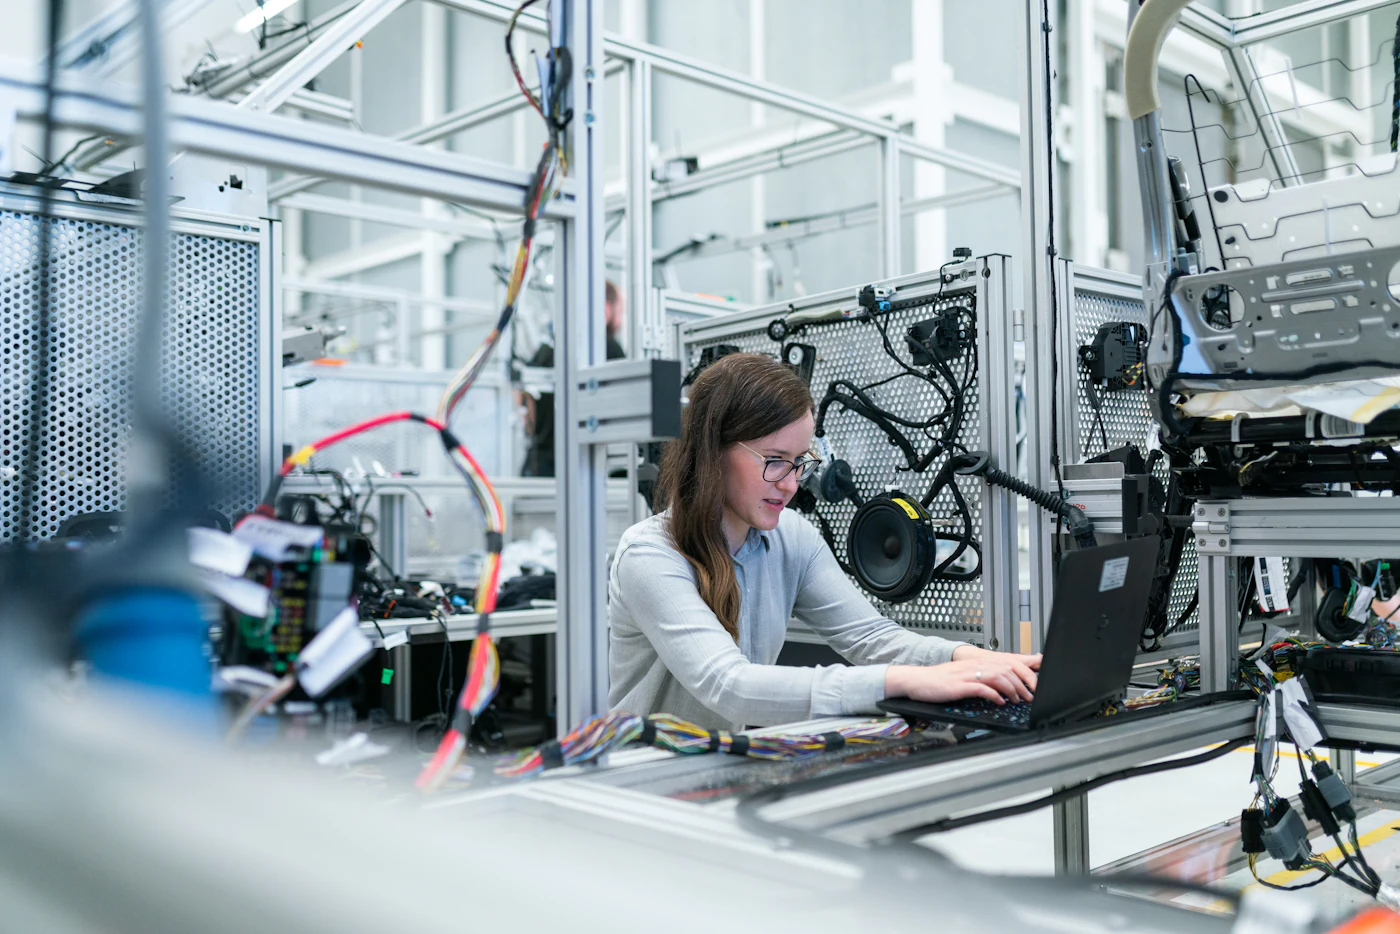
Manufacturing
Converging IT and operational technology, ransomware that halts production lines, and new obligations on connected products make manufacturing uniquely exposed.
ExploreThese are the sectors under the most regulatory and threat pressure, but we serve all sectors. Tell us about your situation.
Proof, not promises
What clients say about working with us.
The way in which teachers teach and students learn is quickly evolving. It was clear that we needed to enhance our security, which Threat Protect helped make a simple and stress-free process, identifying and resolving a number of areas where we could improve our security posture, enabling our teachers and students to operate in a secure environment.
By consolidating security solutions, working with Threat Protect has enabled us to optimise our overall IT spend whilst significantly reducing the management admin involved. I have full trust that any solutions that Threat Protect put forward are in the best interests of the company and our security needs.
Technologies we work with
We hold partnerships across the market so our advice is grounded in real deployment experience, not locked to one stack. A sample of who we work with:

All 33 of our services can be bought through your AWS account, on the AWS bill you already pay.
Browse the services


Need offensive testing?
We arrange deep, tester-led penetration testing and red teaming. Independent testers find the weaknesses; we help you fix, manage and govern them. For broad, regular coverage, start with a vulnerability assessment.
Resources
Clear thinking, free of sales theatre.
PHP2Shell: what the critical PHP vulnerabilities mean for your organisation
Two critical flaws in PHP itself (CVE-2026-109618 and CVE-2026-109619) allow unauthenticated remote code execution and are being exploited. What is affected, why configuration changes are not enough, and the five steps to take this week.
Read
The best MDR providers in the UK: how to build a shortlist that fits
There is no single best MDR provider, only the best fit for your estate, sector and regulator. The four types of MDR provider in the UK market, who each suits, the seven tests that separate them, and how to get from a longlist to a shortlist.
Read
Seven questions to answer before your organisation rolls out generative AI
Generative AI tools are usually adopted before anyone has decided how to govern them. Seven questions to answer first, covering where AI is already in use, what data goes in, what the tools can reach, who checks the output, who owns it and which rules apply, and how to evidence the answers.
ReadOur Values
Transparency
We have the courage to be honest and share information, taking accountability for our actions.
Inclusiveness
We respect and trust one another, regardless of our differences.
Excellence
We strive to be leaders with a commitment to continuous improvement & celebrating our successes.
Let’s talk about where you are, and what comes next.
A 30-minute call with a senior advisor. Bring your situation; leave with at least one useful answer, whether or not we’re a fit.
Book a call